Give the agent room. Keep the boundary.
Concrete setups for the moment when “please be careful” stops being a security plan. Start with the problem that sounds like yours.
Choose a guide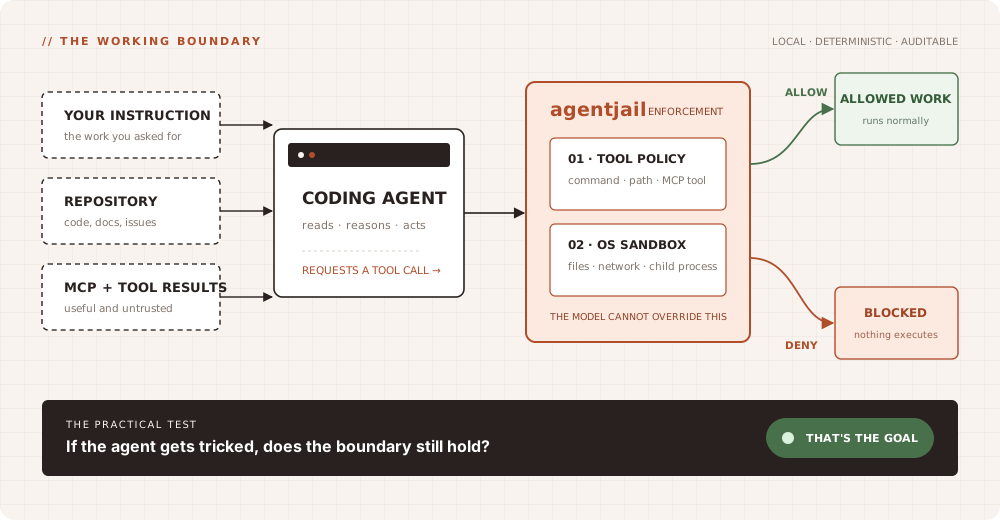
Follow a tool call from request to result.
This is the security model the guides build on. Open the full map to focus nodes, trace routes, or switch views.
Open the full-screen map ↗What are you trying to make safer?
You do not need to read these in order. Each guide starts with a real setup and ends with something you can test.
I want fewer permission prompts
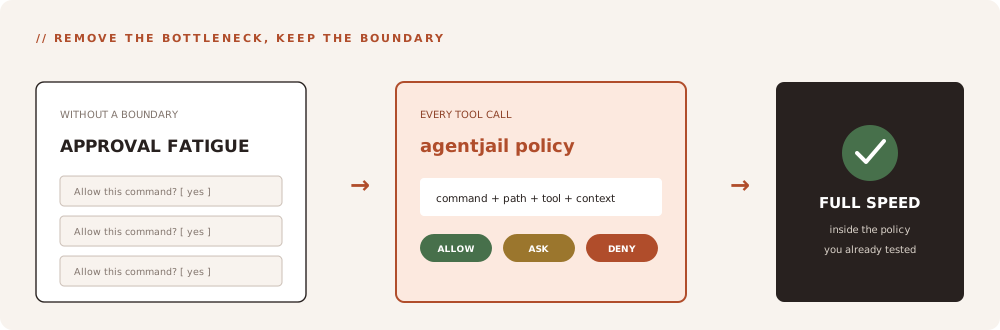
Claude Code: safely skip permission prompts
How agentjail enforces a hard boundary when you run an agent with permission prompts disabled.
Read the guide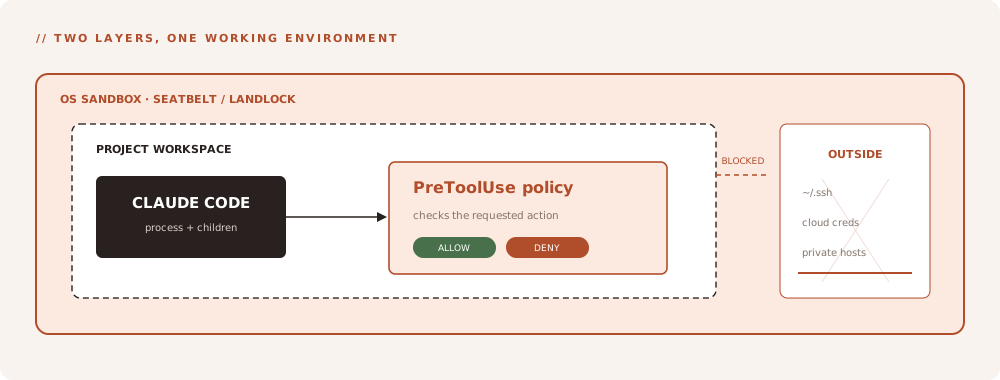
I need to contain Claude Code
Claude Code sandbox
Set up Claude Code with tool policy and OS sandboxing, then test filesystem, network, and MCP restrictions.
Read the guide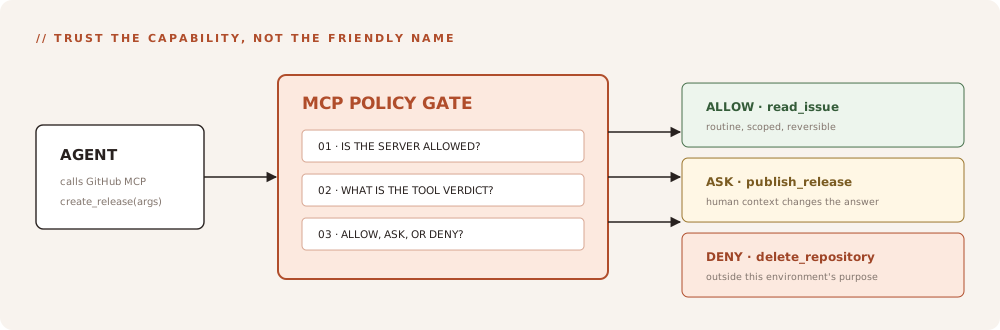
I have MCP servers to review
MCP security guide
Inventory MCP servers, scope individual tools and credentials, and test policy before allowing agent access.
Read the guide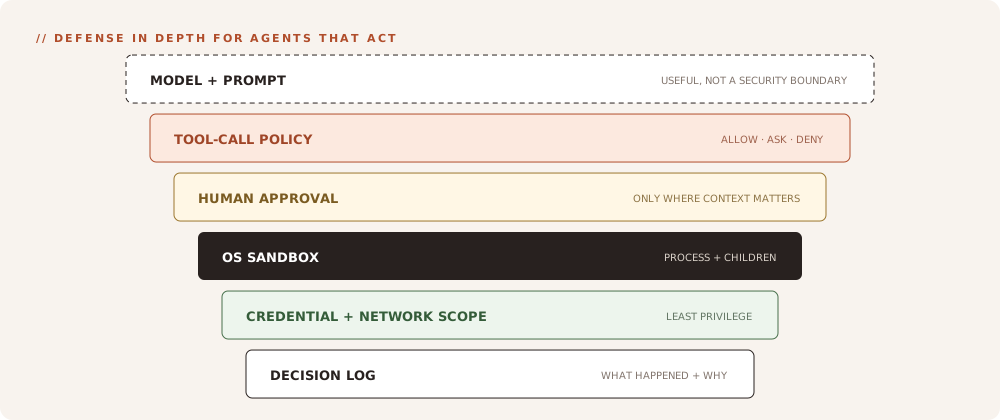
I need the full security model
AI agent security guide
Map a coding agent's permissions, enforce boundaries outside the model, and test the controls that limit mistakes.
Read the guideLooking for flags, config fields, or policy syntax?
Open the full documentation →